1-click MMI execution in Android
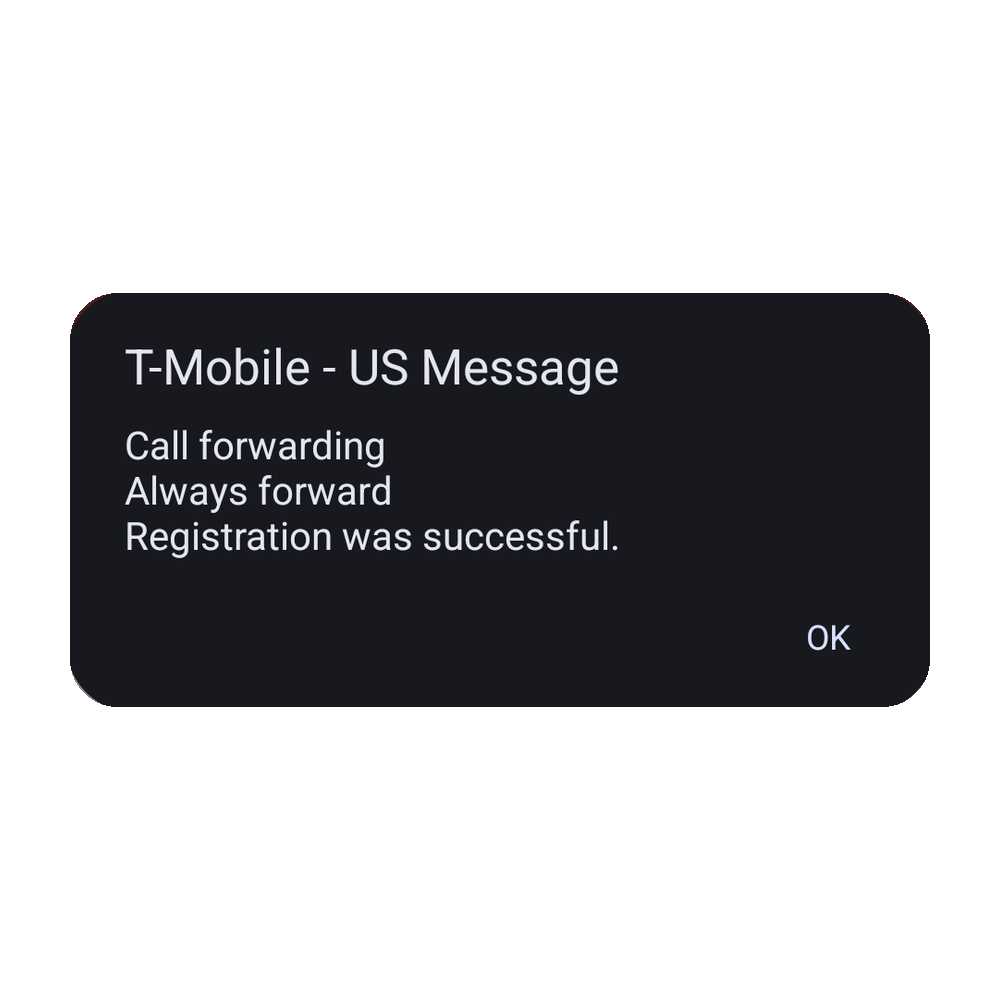
An application with the CALL_PHONE permission can execute carrier MMI/USSD codes with no user confirmation. A vulnerable application with browsable deeplinks can trigger MMI execution with a single tap.
Karan Saini · Karan Saini